SIEM Use Case Guide – Part 3

Real World Examples

In this section let’s take the real world example of Bloodhound and discuss defensive measures for that use case.

Bloodhound

Step 1: Know thy Enemy.

Have a good list of threat intelligence sites (eg Mitre) that you can use to learn about an attack group or a specific exploit. Bloodhound uses ‘ingestors’ like Sharphound to collect information which it then uses to map out an attack path. So when looking for defenses you may need to look at the ingestors, not Bloodhound itself (although Sharphound may run as a sub-command within Bloodhound).

Step 2: Plan your defenses and build a Blue Team toolkit.

There are many ways to detect and block an exploit, depending on the conditions. But don’t take too much time thinking about the best way to do it when there are some easy wins that you can do right away, for example:

  • Ensure an EDR (and AntiMalware) is installed on all endpoints, and run reports to ensure their rules/signatures are all kept updated.
  • If the EDR vendor provides advanced features, make sure they’re enabled for optimal defenses – eg. enable blocking mode, enable advanced configurations such as Microsoft Defender ASR (Attack Surface Reduction)
  • Configuration Policies – Use tools like Microsoft Endpoint Manager (with Intune) to configure policies on your endpoints to provide a base ‘hardening’ for your devices. Ensure logging is enabled on all servers, including advanced logging for Powershell. If you’re using 1 or more cloud platforms you should be managing your infrastructure’s security policies with a CSPM (cloud security posture management) like Microsoft Defender for Cloud – this can also add additional defenses like FIM – File Integrity Management.

Step 3: Build Process For Faster Response

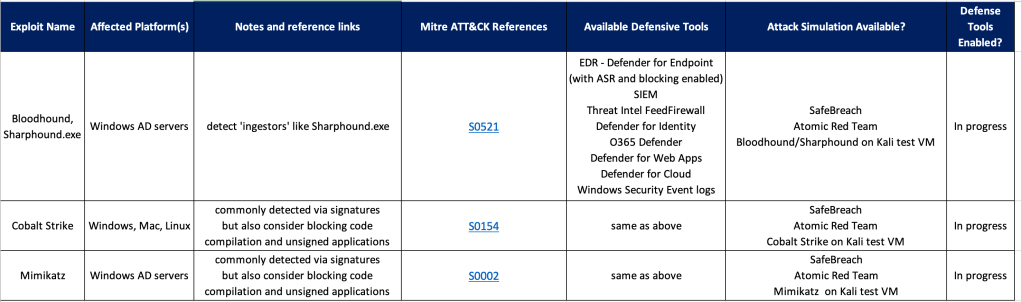
Once you have a list of tools/methods for building defenses, create a checklist and start filling it out. You’ll find that after adding a few rows a common pattern will arise for similar exploits, so your ‘Defender’ job should get a bit easier over time.

Example Defender Framework/Checklist
See also:
Microsoft Ignite 2022 – START HERE

https://news.microsoft.com/ignite-2022-book-of-news/

https://ignite.microsoft.com/en-US/home

The list of Ignite presentation topics is HUGE!!!

Fortunately, Microsoft provides MVPs with an quick reference sheet so we can share our top picks with you.

So here are my top picks for security topics from Microsoft Ignite (and a few other non-security topics):

Rob Lefferts, CVP of PM, Modern Protection and SOC

https://ignite.microsoft.com/en-US/speakers/66804f79-fa68-4762-8f82-45798387e70e?source=/speakers

Shawn Bice, CVP, Cloud Security

https://ignite.microsoft.com/en-US/speakers/0e6b8553-7111-4422-94e0-04a8dddbd678?source=/speakers

What’s new in SIEM and XDR: Attack disruption and SOC empowerment

https://ignite.microsoft.com/en-US/sessions/e1f4b983-55d3-4048-8e90-9c22c4362e6b

Zero Trust as Business Driver: 3 Discrete Scenarios

https://ignite.microsoft.com/en-US/sessions/9974d5a2-b241-4ede-ab2d-c2cd1b7a83be

From Code to Cloud: A new Approach to Integrating Multicloud Security

https://ignite.microsoft.com/en-US/sessions/28f61a40-f1e6-43d8-9fd0-e3c8c6267bac

Secure access and improve efficiency with Microsoft Entra

https://ignite.microsoft.com/en-US/sessions/538bf946-a7bf-46dc-809f-9fbda241f918

Protect Everything, Everywhere With Comprehensive Security

https://ignite.microsoft.com/en-US/sessions/17bbd01d-4e26-4e2e-9eec-3a060b477eda?source=sessions

Azure Arc

https://ignite.microsoft.com/en-US/sessions/50f1092f-6209-4349-b02e-9ad2872ad136?source=sessions

https://azure.microsoft.com/en-us/products/azure-arc/hybrid-data-services/#overview

https://techcommunity.microsoft.com/t5/azure-stack-blog/what-s-new-for-azure-arc-and-azure-stack-hci-at-microsoft-ignite/ba-p/3650949

Azure Monitor

https://techcommunity.microsoft.com/t5/azure-observability-blog/bg-p/AzureObservabilityBlog

Azure – Postman integrations

https://techcommunity.microsoft.com/t5/apps-on-azure-blog/enhanced-api-developer-experience-with-the-microsoft-postman/ba-p/3650304

Supply Chain Management Certification

https://techcommunity.microsoft.com/t5/microsoft-learn-blog/announcing-a-new-dynamics-365-supply-chain-management-functional/ba-p/3250813

Microsoft Cloud for Sustainability

https://cloudblogs.microsoft.com/industry-blog/sustainability/2022/10/12/driving-innovation-for-esg-progress-with-microsoft-cloud-for-sustainability/

Power Automate

https://powerautomate.microsoft.com/en-us/blog/new-ways-to-innovate-with-ai-and-microsoft-power-automate/

Top 5 Cybersecurity Capabilities

5 cybersecurity capabilities announced at Microsoft Ignite 2022

Microsoft Entra

https://ignite.microsoft.com/en-US/sessions/538bf946-a7bf-46dc-809f-9fbda241f918?source=sessions

https://www.microsoft.com/en-us/security/business/microsoft-entra

Microsoft Sentinel

https://techcommunity.microsoft.com/t5/microsoft-sentinel-blog/microsoft-sentinel-what-s-new-at-microsoft-ignite/ba-p/3649968

Microsoft Purview

https://techcommunity.microsoft.com/t5/security-compliance-and-identity/microsoft-purview-information-protection-showcase-of-new/ba-p/3647934

Making Security Fun with Microsoft Cloud Games

This is a really fun way to learns some practical skills with Microsoft Cloud security tools.

I would recommend this for anyone who has a Microsoft E5 license or anyone using Microsoft cloud based products who is ready to get serious about securing their cloud and on-prem environment with Microsoft security tools.

This is not for beginners.

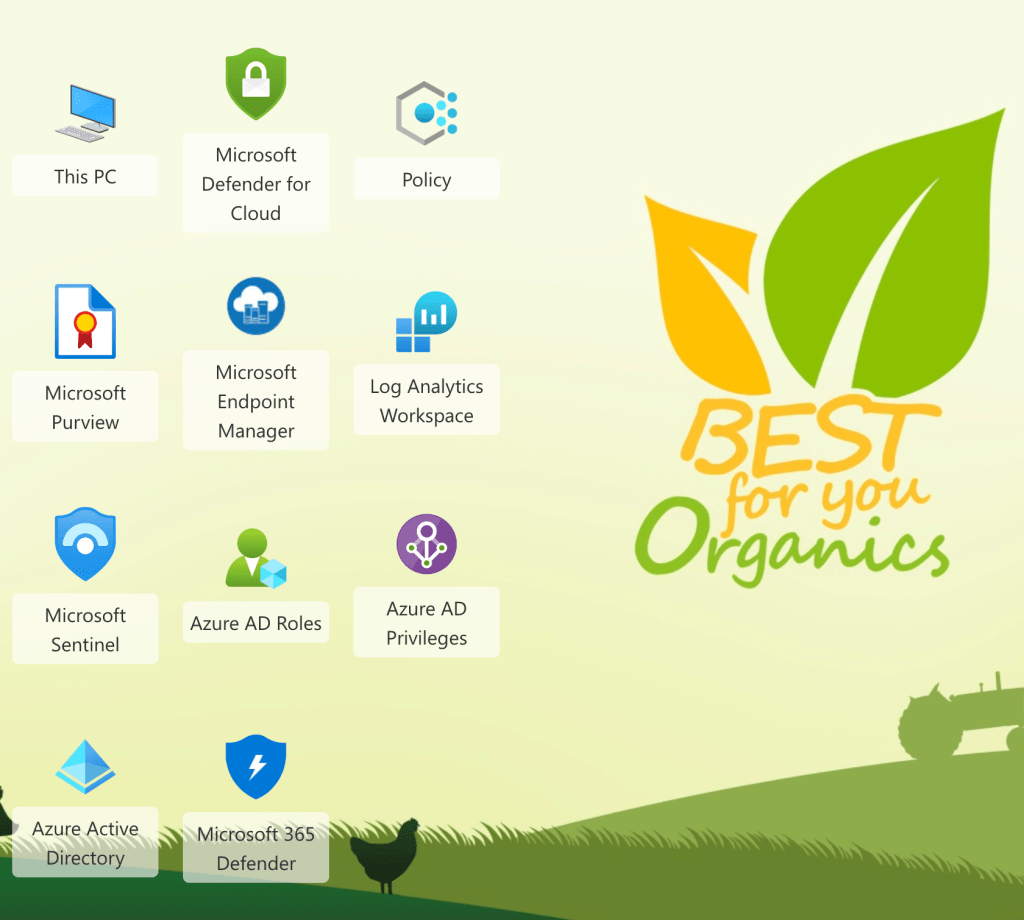
It’s expected you have at least a basic understanding of what these security tools are shown in this screenshot from the game:

Expect to spend at least a couple of hours playing the game.

Have fun!

Performing a Security Audit on Logic Apps

As DevOps move toward no-code apps in the cloud, there becomes a need for security reviews and controls to prevent risky

This is nothing new, but the need for better security reviews is becoming clear as more people try to rush to get their apps done in the easiest way possible.

Here’s a simple approach to identifying security risks in your logic apps:

  1. Create an architecture diagram of your logic app. This can be a simplified version that just shows the high level logic.
  2. Break down the logic app by it’s components:
  • The individual logic app components – you likely won’t find too many security problems here.
  • all the parameters – don’t hardcode passwords into parameters!
  • connectors – Often the culprit of weak security in logic apps. Really understand what these connectors are communicating with. Don’t allow public access. Limit the roles/permissions.
  • app registrations – another culprit of weak security. If app registrations are needed for your logic apps, be sure permissions are set to their most restrictive settings. avoid read.all readwrite.all settings.
  • managed identities – if possible, use managed identities instead of user accounts for your connectors. Many logic apps don’t yet support managed identities, so those apps will require additional monitor and possibly frequent password/secret changes.

3. Use Resource Locks to prevent changes. If someone tries to turn off resource logs be sure it’s logged and alerted on.

4. Restrict user/admin access to your logic apps. Some apps can have really powerful permissions/access, so you don’t want users to ever have the ability to change logic apps unless they’ve been given specific short-term permissions to do so.

5. LOG EVERYTHING – wherever possible, enable logging within logic apps and connectors. Store logs in a Log Analytics Workspace. Use Azure Monitor alerts ore Microsoft Sentinel to monitor/report/alert on all activities.

6. Perform ‘attack simulations‘. Run your logic apps through test conditions which will trigger your alerts. Validate your alerts work as expected.

7. Build a ‘logic app security audit’ spreadsheet. Use this as a template for repeated audits for future logic app security testing. Use the above ideas as the initial framework for your spreadsheet.

Zero Trust – A simple Approach for Azure Enterprises

Zero Trust sounds very enticing, but feels overwhelming as much as any other standards based framework.

However there are some quick wins in the Azure world, and all you need is:

  • A good checklist (The Microsoft Zero Trust Assessment Quiz)
  • A Microsoft Sentinel workbook (see below)

In addition, Microsoft has a ton of direction around Zero Trust like:

If you prefer to save some reading time, I’ve taken Microsoft Zero Trust Assessment Quiz results and compressed it into a clean list of questions here:

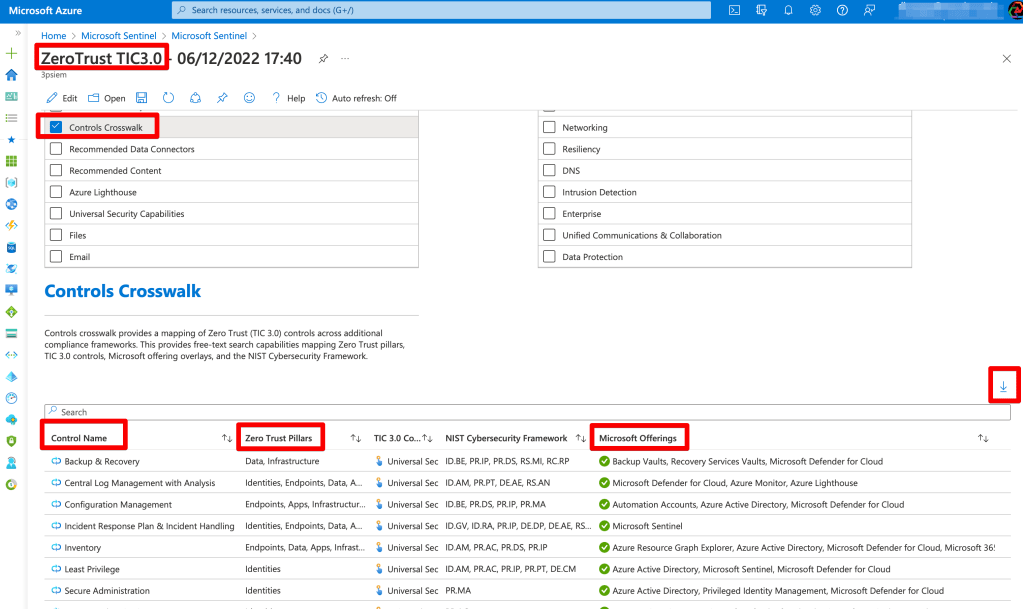
Microsoft has also added a Zero Trust workbook to Azure Sentinel, so if you’re using their SIEM, there’s an excellent report that you can export and have a full list of security tool recommendations that you likely already own (depending if you have an E3 or E5 license)

If you’re familiar with the resources under ‘Microsoft Offerings’ then you can begin planning your Zero Trust controls around these features. If you’re not familiar then now it the time to begin learning and proposing a Zero Trust approach around these tools.

Enjoy!

Mapping Cyber Defense Use Cases to Mitre ATT&CK Data Sources

Mitre ATT&CK provides so many ways to quantitatively think about approaches for defending against attackers.

However it can be challenging to map the ATT&CK matrix to to real-world defense methods.

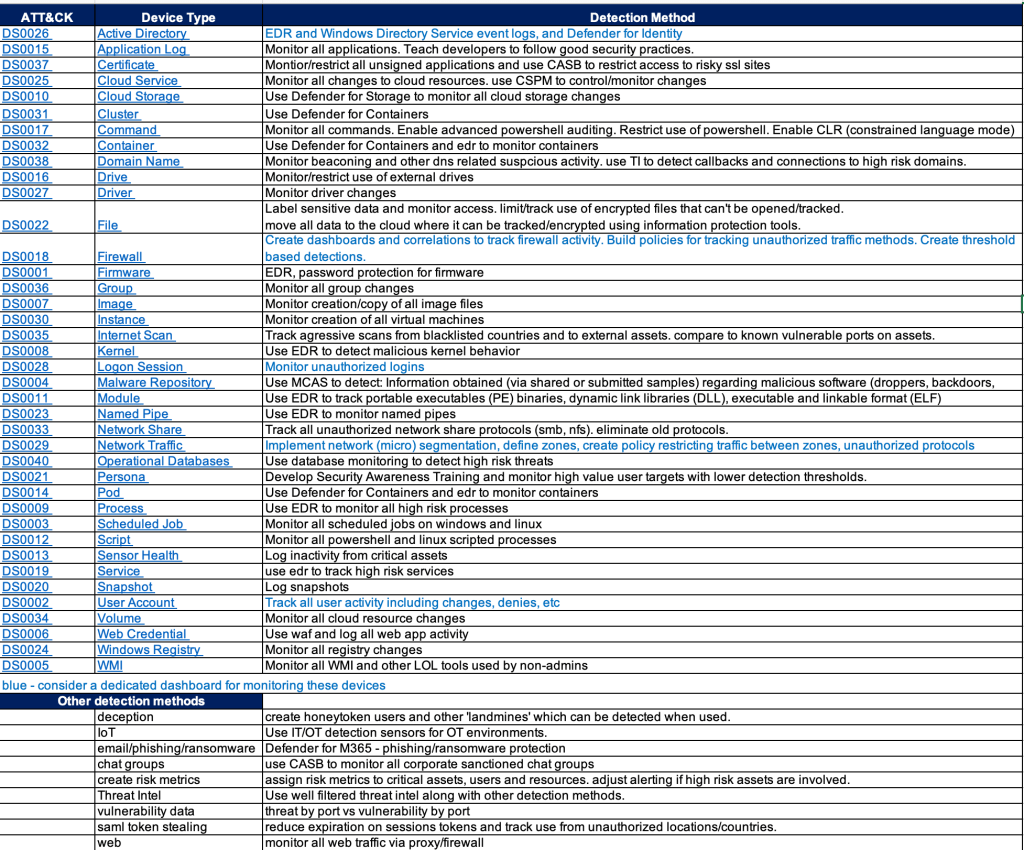
One approach is to look at the ATT&CK data sources and research detections that would map to those data sources.

This still requires some experience and a bit of guessing since there doesn’t appear to be an easy button way to map data sources to detection tools.

Endpoint Detection vendors have done a pretty good job mapping detections to ATT&CK techniques but few of them share their mappings in a simple spreadsheet – that would greatly help validate your detection gaps.

SIEM products like Microsoft Sentinel have done a good job mapping detection rules AND log sources to ATT&CK.

The chart below is an example of an easy way to provide a path forward on where to focus efforts for detections. It also provides a gap analysis for any obvious security tools that may be missing in your environment.

And hopefully my short detection method recommendations will give you some ideas or at least stir conversation.

I’m a Microsoft Recognized Community Hero!

I’m very excited to have been recognized by Microsoft as an Azure Community Hero!

Having worked with (not employed by..) Microsoft for several years as a Security Solutions Advisor/Developer, in 2021/22 I began taking on more of a volunteer role finding ways to give back to the community in any ways I could find.

After several months of contributing on the Microsoft Q&A sites I was very surprised to receive this badge(r) of recognition which they title ‘Microsoft Azure Community Hero’.

So I hope you don’t mind me sharing in my happiness for this honor.

Isn’t it cute?

https://jumpnet.enjinx.io/eth/asset/68c0000000000065/183?source=EnjinWallet-1.15.1

Using OpenAI as your personal everyday Oracle

My coding skills are enough to get by, but I’ve found new inspiration in everything from how to write better code to how to make better coffee by using the openai playground.

It’s easy, just go to:

https://beta.openai.com/playground

And start typing your questions.

It helps if you are more descriptive on what you want, eg.

‘generate detailed vbs code for copying files over the network to another server’

Sure, you could just find a code generating web site, but there’s a convenience in being able to use simple sentences to describe your needs vs the harsh logic of a google search!

And now you have a new, portable, tool to entertain you during those boring moments in your life…

Enjoy, and welcome to the future..

Installing the Azure Arc Agent for Windows Event Collection(and more)

If your SIEM is Microsoft Sentinel, then you likely need to collect Windows security events.
If you’ve never heard of ‘Arc’ then you’re likely collecting Windows logs using the legacy ‘Log Analytics Agent (Microsoft Monitoring Agent)’.
Microsoft recommends using the Azure Arc agent, along with the Azure Monitoring Agent, which will get push out automatically once configured in Arc, or Azure Monitor, or Sentinel.

The Arc agent extends the security controls you normally only get from cloud servers to your on-prem servers, and simplifies the number of agents needed for on-prem servers to work with Azure.

A discussion about Arc/CSPM/Azure Policy/Defender for Cloud/Asset Inventory/Attack Surface is out of the scope of this article, but trust me, you want to use Arc for all your on-prem windows and linux servers.

Prerequisites for Arc:

  • Local admin access to the on-prem windows/linux server
  • Global Admin access to Azure
  • On-prem server must have Internet access or a direct connection to Azure.
  • Sentinel Log Analytics Workspace

ARC agent installation:

Azure Monitor Agent (AMA) Installation

  • You actually don’t need to install AMA.
  • You configure a ‘Data Collection Rule’ in Sentinel or Azure Monitor with the preferred parameters, and this will enable the AMA as an ‘Arc Extension’

Sentinel Connector AMA Setup

  • Since most of the topics in this blog are around Sentinel, that will be the configuration discussed here.
    • You can also configure this in Azure Monitor and in Azure Arc, but the data might not then be accessible as easily in Sentinel (it may get stored in the Events table vs the SecurityEvents table – see references below)
  • In Sentinel go to: Connectors > “Windows Security Events via AMA”
  • Create a ‘Data Connection Rule (DCR)’:
    • Add your servers
    • Select the ‘Common’ filter – this is the best choice for all of the Security Events.
  • After a few minutes you should see your on-prem security events in the SecurityEvents table.

References:

https://docs.microsoft.com/en-us/azure/azure-monitor/faq#azure-monitor-agent

https://docs.microsoft.com/en-us/azure/azure-monitor/agents/azure-monitor-agent-windows-client

Blue Teaming – My Top 10 Solutions for a Successful SOC Defense Strategy

(in no particular order – includes both on-prem and cloud)

SIEM Attack Simulations and tuning
Configure test lab and simulate attacks to verify triggering of alerts

Active Defenses/Deception Techniques
Plan/Deploy/Test deception techniques

Use Case Catalog
Documented methodology for providing clear/concise implementation of SIEM use cases based on existing log sources and a focus on threat and compliance related detections.

SDLF – Security Data Logging Framework
Documented methodology for providing clear/concise implementation of log sources into SIEM for assured value. (perhaps I need to blog about this)

Cloud Diagnostic Checklist
Checklist of O365 and Azure security features to improve awareness of security features available with an E5 license.

Purple Teaming
Red/Blue teaming activity with a focus on improving awareness of SOC security best practices.

Attack Surface Mapping
Network and asset discovery discussions with a focus on attack surface mapping

EDR attack simulations
Setting up attack simulations for your EDR

SOAR Development
Creation of automated actions to both enhance SIEM alert details and provide automated actions as a result of a given incident.

Cloud Security Posture Planning and development
Planning and deployment of CSPM/CWPP